 PickVids
Best Security & hacking Videos
「Security & hacking」下面有192部被不同的人、在不同月份推荐过的视频。挑的时候先看对象:入门7部,适合还没学过的人;进阶63部,适合已经懂术语的人;普通向85部,按兴趣就能看;更硬的37部,留给想看推导或细节的人。这一类数量最多的是演讲,所以它们的共同点是一位讲者把一个判断讲完,例子是为了撑住这个判断。常出现的频道包括DEFCONConference、media.ccc.de、Black Hat。目录给这个主题划的范围是:Computer security: vulnerabilities, exploits, malware, reverse engineering, CTF, penetration testing, Black Hat and DEF CON talks, OS security, memory safety, zero-days, responsible disclosure.如果只看三部,就从《Behind the Scenes of iOS Security》开始,它负责把问题讲出画面;然后看《Why Electronic Voting Is Still A Bad Idea》,换一种讲法或例子;最后看《USENIX Security '18-Q: Why Do Keynote Speakers Keep Suggesting That Improving Security Is Possible?》,留给已经有基础的人。页面按每页24部切开,顺序看的是被推荐跨越了多少个月,不是播放量。每条标题下面那一句是这部片子自己的内容说明,用来区分它在讲定义、过程、演示还是观点。点进去能看到推荐原话、原文链接和适合谁看。看的时候把强烈推荐当成有人明确叫你去看,把引用当成只是拿来举例,把批评留下来对照,不要把每条评论都当成同一力度。

Tobias Engel: SS7: Locate. Track. Manipulate.
Tobias Engel's 31C3 talk shows how weaknesses in the SS7 telephone signaling network let companies and attackers locate, track and manipulate phones from anywhere in the world, with precision down to about 50 meters.

H2K2 (2002): "The Conscience of a Hacker"
The Mentor (Loyd Blankenship) reads his 1986 essay "The Conscience of a Hacker" at H2K2 in 2002 and adds his own insight about its backstory.
STOP Buying ANDROID TV Boxes!
Linus Tech Tips warns against cheap Android TV boxes, many of which ship with preinstalled malware.

OffensiveCon19 - Alex Ionescu - Keynote - Reversing Without Reversing
Alex Ionescu's OffensiveCon 2019 keynote on how reverse engineering is done on Windows without conventional reversing.

NVIDIA — Securing the Future of Safety and Security of Embedded Software (Captioned)
An AdaCore webinar in which NVIDIA engineers explain why and how they adopted Ada and SPARK for security-critical firmware.

[756] Sentry Safe Cut in Half FAST!
LockPickingLawyer shows a Sentry fire safe being cut in half with a saw in a few minutes.

36C3 - A systematic evaluation of OpenBSD's mitigations
A 36C3 talk that systematically evaluates OpenBSD's exploit mitigations, asking how effective they really are and what they cost in performance, complexity and inspectability.

DCEmu Reviews - 27C3 - Chaos Communication Congress 2010 - fail0verflow - FULL VIDEO
The fail0verflow 27C3 talk on breaking PS3 security, covering how Sony's implementation failed, including its ECDSA mistakes.

DEF CON 23 - Robinson and Mitchell - Knocking my neighbors kids cruddy drone offline
A DEF CON 23 talk on researching whether a commercial quadcopter could be forced to land by interfering with its GPS signal, inspired by a neighbor's kid's drone.

Ochko123 - How the Feds Caught Russian Mega-Carder Roman Seleznev
A Black Hat USA 2017 briefing by the prosecutors who caught Russian carder Roman Seleznev.

AI slop attacks on the curl project - Daniel Stenberg
Daniel Stenberg's keynote at FrOSCon 2025 on AI slop attacks on the curl project, with examples of bogus AI-generated security reports.

Black Hat 2013 - Exploiting Network Surveillance Cameras Like a Hollywood Hacker
Craig Heffner's Black Hat 2013 talk on exploiting network surveillance cameras, covering how insecure their firmware is.
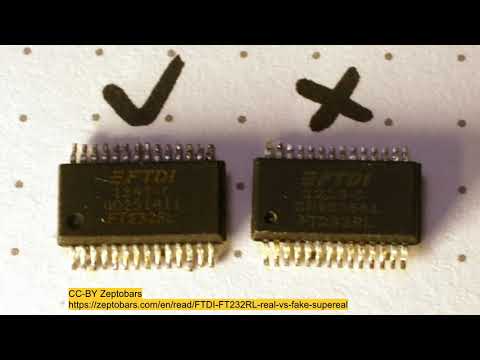
35C3 - Modchips of the State
A 35C3 talk presenting a proof-of-concept SPI bus hardware implant with capabilities like those alleged in the Bloomberg Supermicro story, plus countermeasures for detecting such modchips.

Defcon 18 - Practical Cellphone Spying - Chris Paget - Part.mov
Chris Paget's DEF CON 18 talk on practical cellphone spying, showing how GSM traffic can be intercepted with a fake base station.

Is It Time to Rewrite the Operating System in Rust?
Bryan Cantrill's QCon SF 2019 talk asking whether operating systems should be rewritten in Rust.

Lest We Remember: Cold Boot Attacks on Encryption Keys
A short Princeton CITP video describing cold boot attacks, where encryption keys remain in DRAM after power loss and can be recovered.

DEF CON 23 - Marc Rogers and Kevin Mahaffey - How to Hack a Tesla Model S
A DEF CON 23 talk by Marc Rogers and Kevin Mahaffey walking through the architecture of the Tesla Model S, what Tesla got right and wrong, and how the interconnected systems can be hacked.
DEF CON 17 - Deviant Ollam - Packing and the Friendly Skies
Deviant Ollam's DEF CON 17 talk explains how legally checking a firearm in luggage can be the most secure way to fly with valuable tech.

Theo de Raadt (ruBSD 2013)
A roughly 14-minute interview with OpenBSD founder Theo de Raadt at ruBSD 2013.
Passkeys in Action | FIDO Alliance Demo Video
A FIDO Alliance demo with Google and Microsoft engineers showing passkeys working across operating systems, browsers, and devices.

DEFCON 19: Introduction to Tamper Evident Devices
A DEF CON 19 talk by datagram introducing tamper-evident devices.

Trusted Computing? Yes or No
A four-minute 2006 explainer on trusted computing, describing what it is and whether users should support it, with a skeptical DRM angle.
DEFCON 21 - DNS May Be Hazardous to Your Health - Robert Stucke
A DEFCON 21 talk by Robert Stucke on DNS errors caused by single-bit flips, which lead to requests for misspelled domains.

The State of Kernel Self Protection Project by Kees Cook, Google
Kees Cook of Google gives a Linux Foundation talk on the Kernel Self Protection Project, which aims to harden Linux against attackers.